*Important Note : Fees are subject to Singapore's prevailing Goods and Services Tax (GST).
1752192000000
60

Cloud & Infrastructure
Cybersecurity & Risk Management
Artificial Intelligence & Automation
Data Analytics & Data Science
Digital Skills & Office Productivity
Project Management & Agile
Software Development & IT Ops
Critical Core Skills
Maritime
Cloud & Infrastructure
Cybersecurity & Risk Management
Artificial Intelligence & Automation
Data Analytics & Data Science
Digital Skills & Office Productivity
Project Management & Agile
Software Development & IT Ops
Critical Core Skills
Maritime
 Cybersecurity
Enrol now and save $0 on your course fee
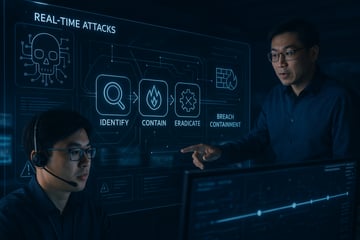
Cybersecurity threats are evolving rapidly, and the ability to proactively detect and respond is essential. This course equips participants with hands-on skills in threat analysis, vulnerability management, and security operations. They will use industry-standard tools to identify threats, analyse data, and recommend countermeasures across hybrid environments.
Learning Outcomes:
Understand threat intelligence and security monitoring practices
Apply behavioural analytics to detect cybersecurity incidents
Analyse security alerts and recommend response actions
Implement vulnerability management and compliance controls
Key Topics:
Threat detection and security intelligence
Behavioural analytics and SIEM platforms
Vulnerability management and remediation
Incident response and risk mitigation
Exam Details
This course is designed to build participants’ understanding of key concepts and domains covered in the CompTIA Cybersecurity Analyst (CySA+) certification.
The CySA+ certification validates the skills required to leverage intelligence and threat detection techniques, analyse and interpret data, identify and address vulnerabilities, suggest preventative measures, and effectively respond to and recover from incidents. It meets the ISO 17024 standard and is approved by the U.S. Department of Defense to fulfil Directive 8570.01-M requirements.
The latest version of the exam, CS0-003, reflects current trends and technologies such as threat intelligence, SIEM, EDR, XDR, and managing hybrid environments. This version replaces the retired CS0-002 exam and focuses on updated methods, tools, and modern threat landscapes.
The certification is suitable for job roles including IT Security Analyst, SOC Analyst, Vulnerability Analyst, Cybersecurity Specialist, Threat Intelligence Analyst, and Security Engineer.
Please note that the certification exam is not bundled with the course and must be purchased separately.
To maximise success, participants are strongly encouraged to complement the course with additional self-study, revision of course materials, and dedicated practice before attempting the exam.
Lesson 1: Explaining the Importance of Security Controls and Security Intelligence
Lesson 2: Utilizing Threat Data and Intelligence
Lesson 3: Analyzing Security Monitoring Data
Lesson 4: Collecting and Querying Security Monitoring Data
Lesson 5: Utilizing Digital Forensics and Indicator Analysis Techniques
Lesson 6: Applying Incident Response Procedures
Lesson 7: Applying Risk Mitigation and Security Frameworks
Lesson 8: Performing Vulnerability Management
Lesson 9: Applying Security Solutions for Infrastructure Management
Lesson 10: Understanding Data Privacy and Protection
Lesson 11: Applying Security Solutions for Software Assurance
Lesson 12: Applying Security Solutions for Cloud and Automation
Who Should Attend This CompTIA CySA+ course?
This course is designed for information assurance professionals who perform job functions related to the development, operation, management, and enforcement of security capabilities for systems and networks. This course is designed for personnel performing IA functions, establishing IA policies, implementing security measures and procedures for information systems and networks.
Pre-requisite
To ensure your success in this course, you should meet the following requirements:
You can obtain this level of skills and knowledge by taking the following courses or by passing the relevant exams:
We’re here to help — reach out anytime.
By submitting this form, you consent to be contacted via email and/or your mobile number regarding your enquiry. You consent to the collection, use, disclosure and processing of your personal data in accordance with our Personal Data Policy.